Stop sending production secrets over Slack
Most small teams hand out production secrets in chat. Moving them to one managed store takes an afternoon.
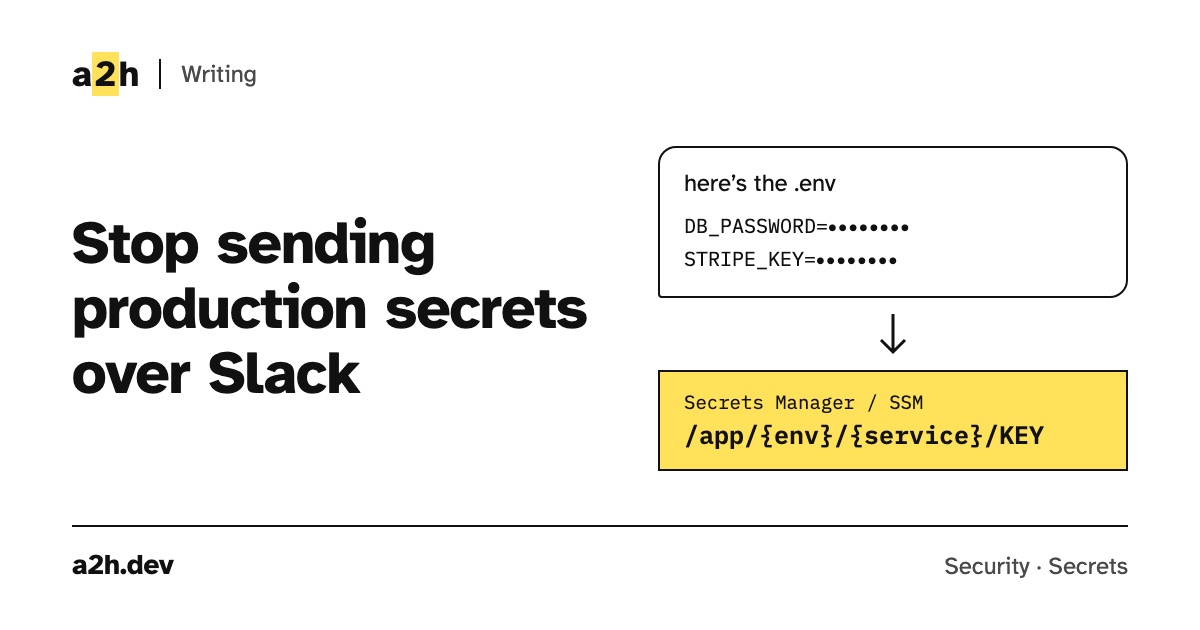
Somewhere in your company’s Slack right now is a DM that says “here’s the .env”, with your production database password attached.
Every small company runs the same secret distribution system: a senior dev pasting credentials into chat. The .env.example with two real values in it. The token sitting in a CI log. The contractor who left 8 months ago and still holds every credential, because rotating felt like a quarter-long project so nobody rotated anything.
This persists because it works, until it very suddenly doesn’t.
The reframe that unblocks it: the dangerous part isn’t missing rotation. It’s hand-distributed secrets in a dozen uncontrolled places. Fixing that is one afternoon:
- Inventory: grep repo + CI for secrets, list each one and what consumes it (30 min)
- One source of truth: SSM Parameter Store or Secrets Manager, named
/app/{env}/{service}/KEY(1 hr) - Runtime injection via ECS task defs or external-secrets, never baked into images (1–2 hrs)
- IAM scoped so each service reads only its own path (30 min)
- Delete the .env files, add gitleaks to CI as a tripwire (30 min)
Then rotate just the 2–3 scariest credentials today. Automate the rest later.
The goal isn’t vault perfection. It’s that no human ever needs to possess a production secret to deploy.
How does your team actually distribute secrets today, honestly?
Written by Abdullah Abdelrazek. Questions, or found something similar?
Reply by email